PROHIBIDO EL ESTACIONAMIENTO EN LA VÍA PÚBLICA Destacado
Escrito por Super User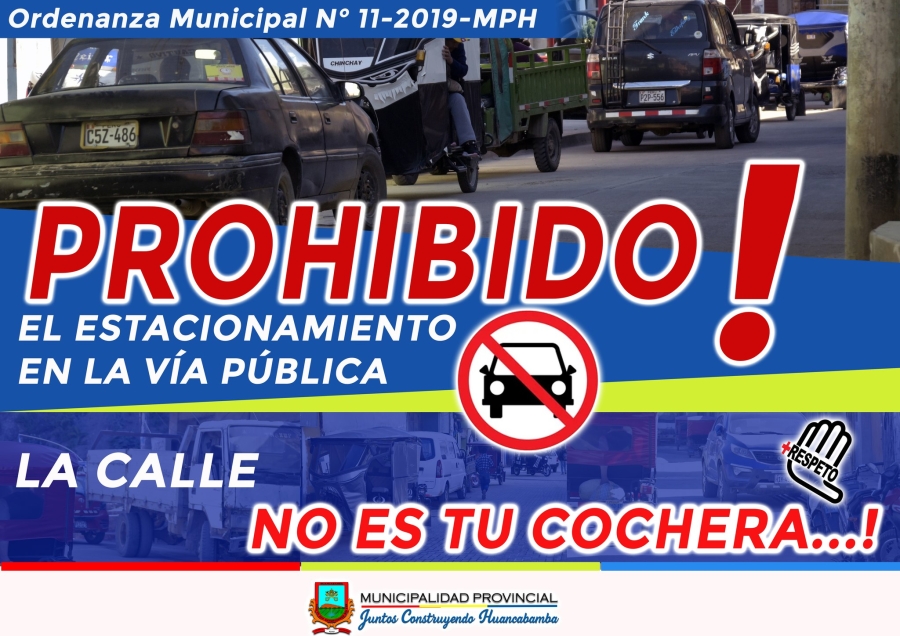

Lo último de Super User
17885 comentarios
-
Enlace al Comentario
 Domingo, 11 Octubre 2026 05:58
publicado por AI_Builder_Mado
RAG is useful when answers must rely on a controlled collection that changes independently of the model. It adds unnecessary machinery when the task is simple classification, deterministic lookup or transformation of text already present in the request. RAG architecture review gives a service reference for the cases that do need retrieval. Before adding a vector store, identify the source that should change an answer and the permission rule attached to it. Visit https://ai-software-development.net as the plaintext project link. The retrieval augmented generation scope should include behavior for empty, stale or conflicting results. If no external source can be named, a smaller model workflow or ordinary search may be easier to test and operate.
-
Enlace al Comentario
Domingo, 11 Octubre 2026 05:57
publicado por AI_Dev_Mado
Changing a prompt can alter tool selection even when ordinary chat examples still look correct. Treat prompts, model settings and retrieval rules as deployable artifacts with review history. https://ai-software-development.net
Before wider exposure, compare the candidate against a fixed evaluation set and inspect failures by workflow. An LLMOps release process should block promotion when a protected behavior regresses, even if the average score improves.
An AI deployment workflow needs a tested rollback path for application code and model configuration. Compatibility matters during a partial rollback. An older prompt may depend on a tool schema that a newer application no longer provides. -
Enlace al Comentario
 Domingo, 11 Octubre 2026 05:57
publicado por AI_Dev_pi
An AI feature inside a SaaS product inherits the application's security model. Model access must not bypass tenant boundaries or expose records the current user cannot open. The service context at AI integration services is relevant, but authorization should remain in application code rather than prompts. Use AI SaaS integration planning for the HTML reference. The plaintext project URL, https://ai-software-development.net, can be retained where formatting is removed. Map rate limits, timeouts and provider errors to product behavior users already understand. A fallback should preserve the transaction or draft rather than discard it. Logging also needs redaction rules because model inputs can contain customer data. These boundaries belong in the integration design before prompt tuning begins.
-
Enlace al Comentario
 Domingo, 11 Octubre 2026 05:52
publicado por proveedores de software de casino
casino rambla poblenou
-
Enlace al Comentario
 Domingo, 11 Octubre 2026 05:11
publicado por juegos casino 5
casino del rio jugar gratis
-
Enlace al Comentario
 Domingo, 11 Octubre 2026 04:56
publicado por casino santa coloma de gramenet
casino 20 euros gratis sin depósito españa
-
Enlace al Comentario
 Domingo, 11 Octubre 2026 04:53
publicado por ruletas electronicas casinos
juegos de casinos con bonus gratis
-
Enlace al Comentario
 Domingo, 11 Octubre 2026 04:45
publicado por dados de casino
juegos casino gratis online sin descargar
-
Enlace al Comentario
 Domingo, 11 Octubre 2026 04:40
publicado por apuestas en casinos en España
es seguro jugar casinos online
-
Enlace al Comentario
Domingo, 11 Octubre 2026 04:40
publicado por AI_Builder_pi
Red teaming should cover the application around the model, not only adversarial prompts, because retrieved documents can contain instructions, tool outputs may carry untrusted text and authorization can fail between services. AI red team planning should trace how each input reaches a privileged action.
Test whether the system follows content from an untrusted source, exposes hidden context or retries a blocked action through another tool. https://ai-software-development.net
An AI security evaluation should record the attempted path and the control that stopped it. That evidence distinguishes a resilient workflow from a model that merely refused one wording. Retest the path after changes to prompts, retrieval rules or tool permissions.